


Federal agents seized approximately 100 devices from North Texas homes as part of a broader crackdown on a network that helped North Korean workers obtain remote IT jobs at U.S. companies using stolen or false identities.
The Justice Department and FBI announced the results of Operation Lonestar Roundup on Tuesday. Agents searched more than 40 residences across Texas in late September and seized roughly 187 laptops and related devices statewide. About 100 of those devices came from the North Texas area. The operation targeted what authorities called “laptop farms,” where U.S.-based facilitators housed and configured company-issued computers so North Korean workers overseas could access them remotely.
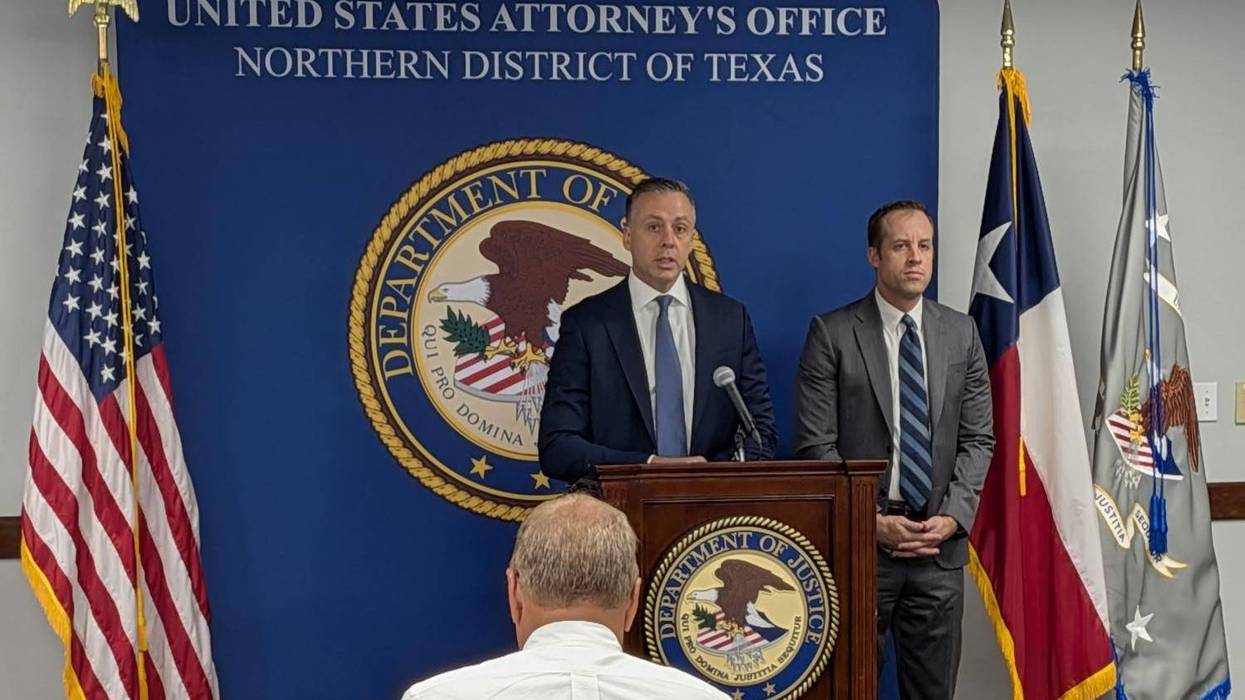
U.S. Attorney Ryan Raybould for the Northern District of Texas said the investigation exposed a system designed to steal American identities, infiltrate American businesses, and siphon wages. FBI Dallas Special Agent in Charge R. Joseph Rothrock said each seized laptop potentially represents a company that hired a North Korean IT worker. Officials said the workers used stolen or fabricated identity documents, virtual private networks, and other tools to appear as if they were located inside the United States. Earnings were then transferred to accounts controlled by North Korea.
SAC Rothrock spoke at a press conference announcing the results of Operation Lonestar Roundup, an enforcement action conducted across the state of Texas that resulted in the seizure of approximately 187 laptops and devices. More than 100 of those devices were seized in the North Texas area. These devices are tied to a hosting network that enabled Democratic People's Republic of Korea IT workers to unlawfully access U.S. corporate systems using stolen or falsified American identities. Learn more at: https://t.co/51YZTxDaKh
— FBI Dallas (@FBIDallas) October 13, 2026
Prosecutors charged 14 individuals in connection with the scheme and announced two arrests. The multi-year effort targeted more than 70 U.S. companies and generated at least $3 million for the North Korean regime in this operation alone. The U.S. Treasury Department has estimated that similar North Korean IT worker schemes generate up to $800 million annually, with a large share of the wages directed to the country’s weapons programs.
Authorities described the affected companies as victims and noted that the rise of remote work has made this type of infiltration easier. The investigation remains ongoing. The FBI has asked companies or individuals with information about the network to report it through the Internet Crime Complaint Center at ic3.gov.
FBI Dallas posted about the operation on X, noting that more than 100 of the seized devices came from the North Texas area and were tied to a hosting network that enabled North Korean workers to access U.S. corporate systems using stolen or falsified American identities.
LISTEN on the Audacy App
Tell your Smart Speaker to "PLAY 1080 KRLD"
Sign Up to receive our KRLD Insider Newsletter for more news
Follow us on Facebook | Twitter | Instagram | YouTube